Trustcenter
Can I trust the software in my organization?
AI-driven trust enforcement of applications, and components.
What our customers love about us
Real-time tracking of attestations and vendor risk profiles.
Risk management
Know in real time new threats arising from existing in-house developed and external applications.
Focus on real threats
Filter out real threats by eliminating false positives.
SCA assessment
Get a real-time risk score for your applications with reachability analysis.
Effective enforcement
Bring discipline into your CI/CD to effectively exclude unknown or unsafe components.
Application risk profile
Create and maintain a software risk profile for compliance, audit, and regulatory adherence.
Real-time
Continuously track attestation, application and stack risk profile.
Actions
Point to actions to take to reduce the risk of vulnerabilities or exploits.
Integration
Trustcenter integrates into dozens of DevOps platforms, monitoring tools, programming languages, and cloud infrastructure.
Trustcenter/Enterprise
- Identification and tracking of artifacts
- World class SBOM management
- Attestation management and distribution
- Risk scoring for your apps
- Compliance with cybersecurity regulations
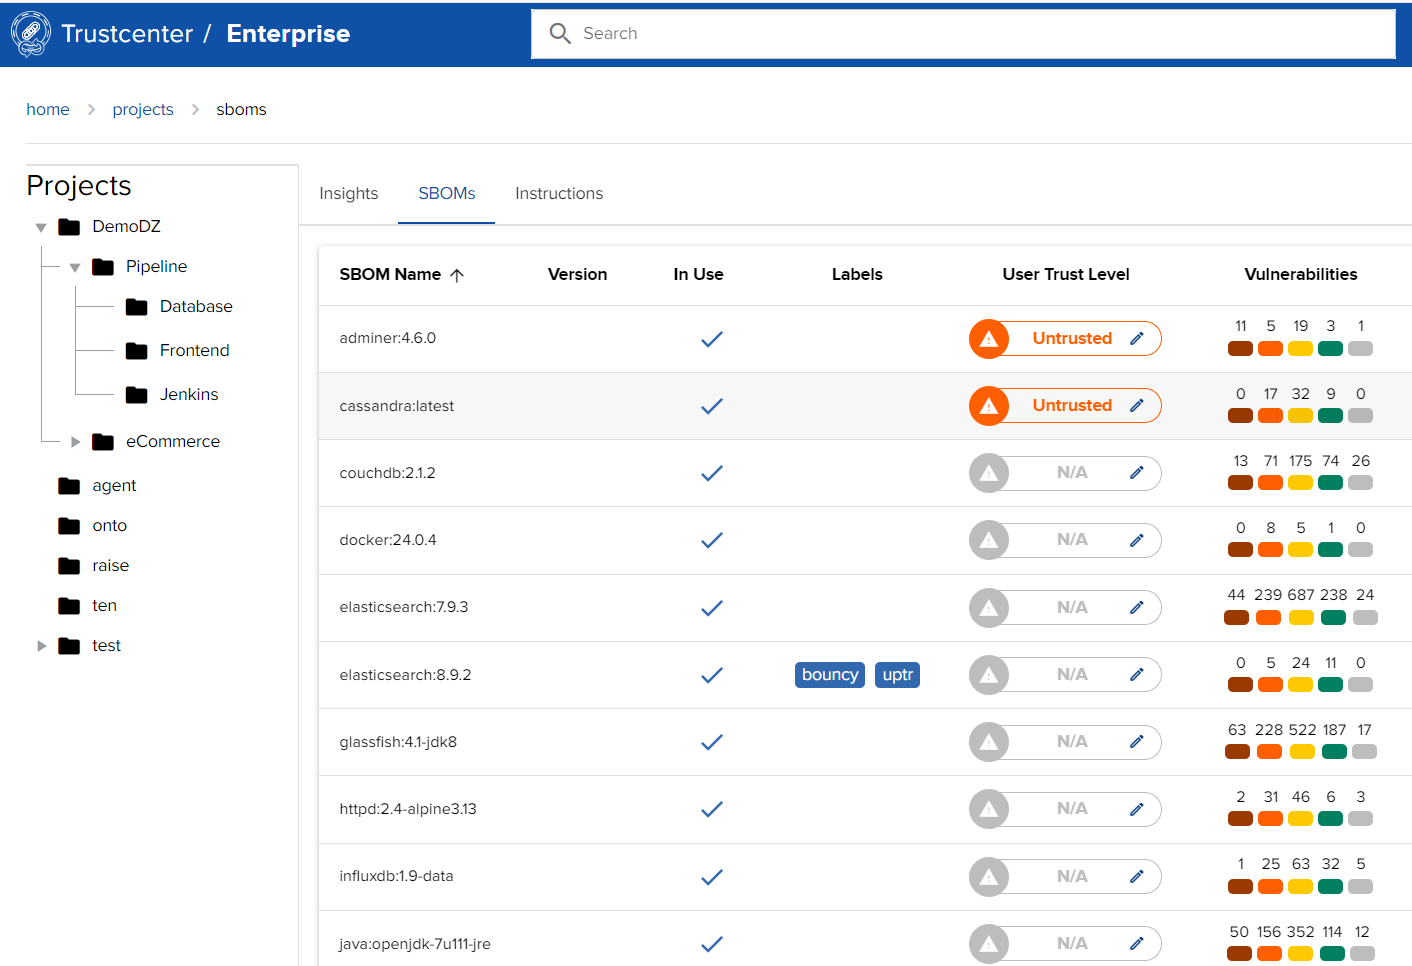
Industry leading SBOM Management
Secure the integrity of software supply chains and all the components used.
Import and export SBOMs from any format to any format. Generate detailed SBOMs for open source applications or containers. Analyze and gain new insights from your SBOMs.
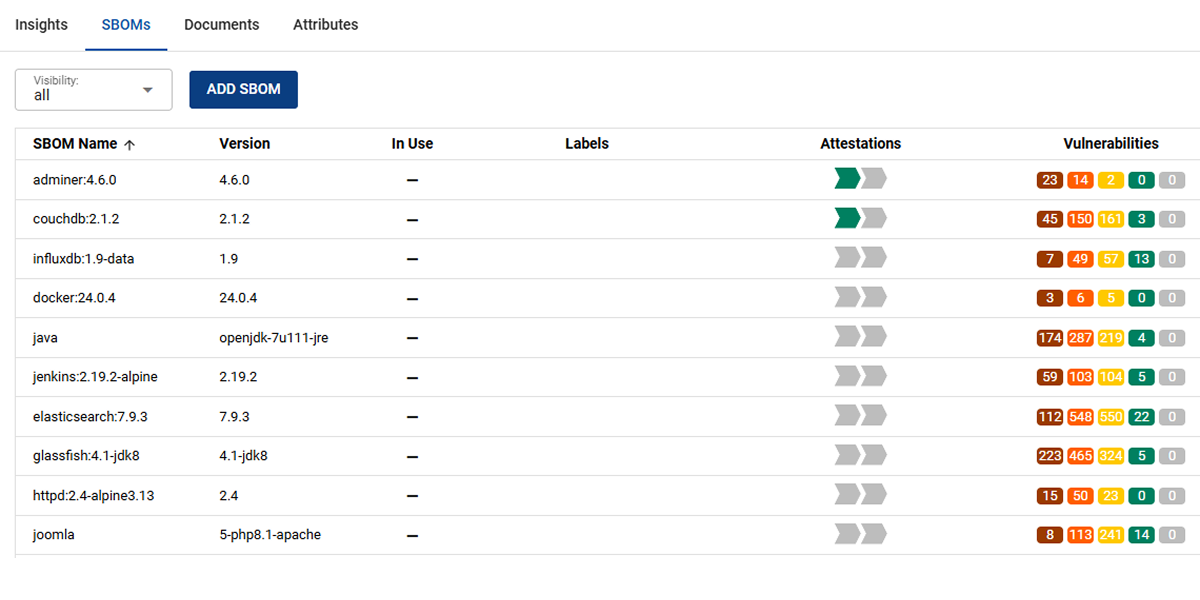
Trusted artifacts exclusively
Only bake components into their applications that are known and trusted.
Unauthorized access to software repositories and build systems allows attackers to insert malicious code and components into software to be released. Trustcenter alerts you whenever unknown and/or untrusted components are detected!
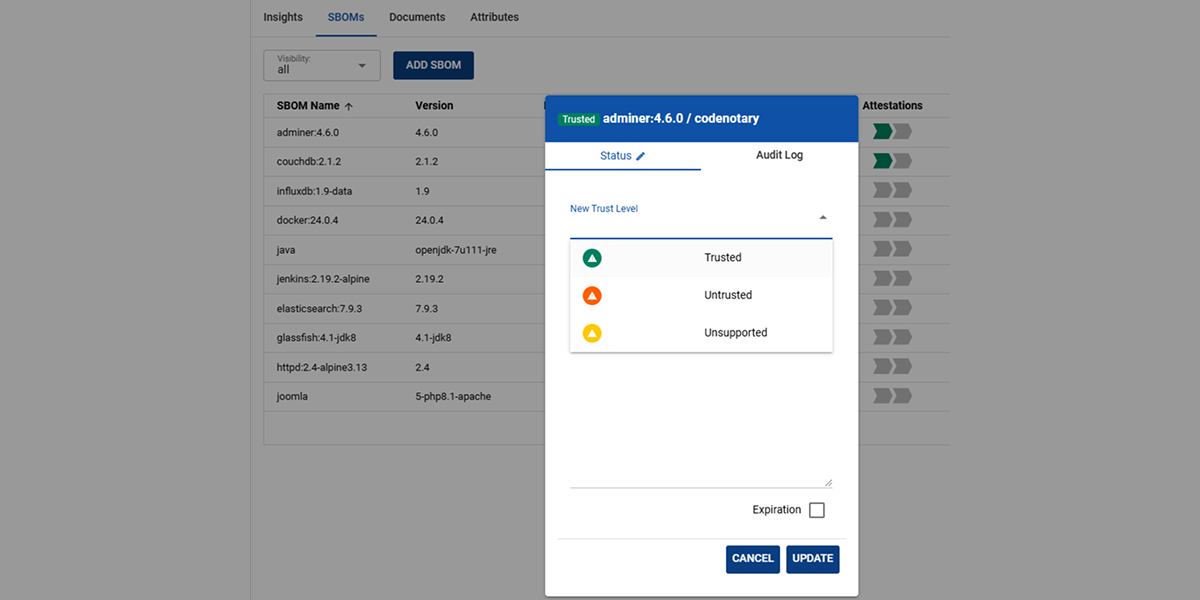
Track your components
Trustcenter supports billions of artifacts!
Discover and catalog your workloads across all environments and track the state of all the components in your software projects and their dependencies.
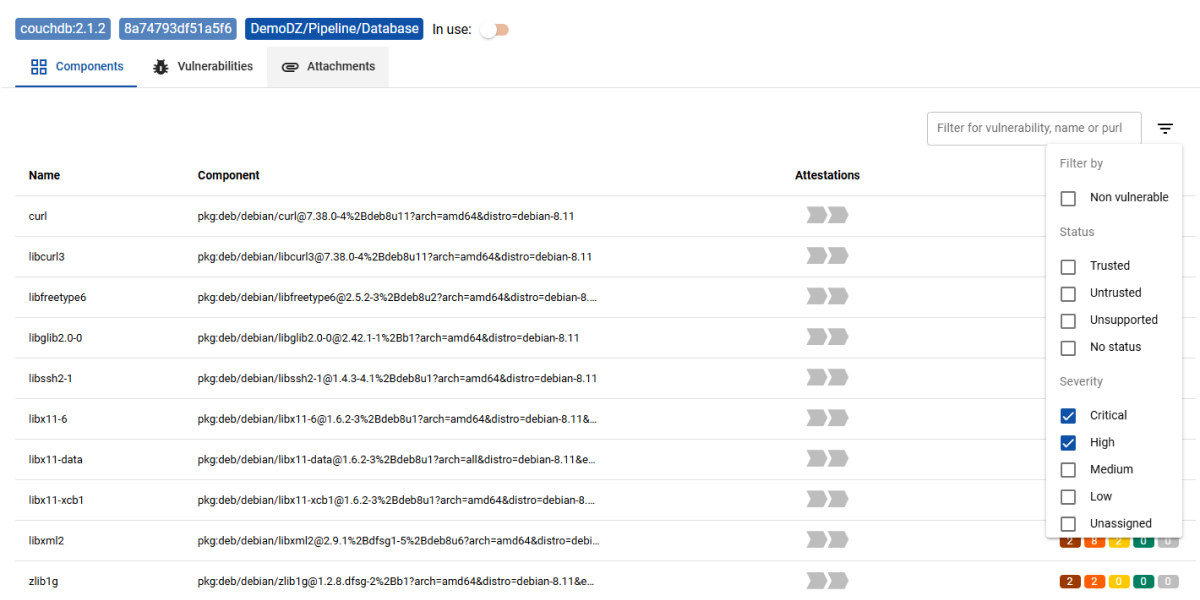
Continuous enforcement
Re-evaluate all components continuously at rest and at runtime.
Enforce the deployment of container images built with known and trusted components.
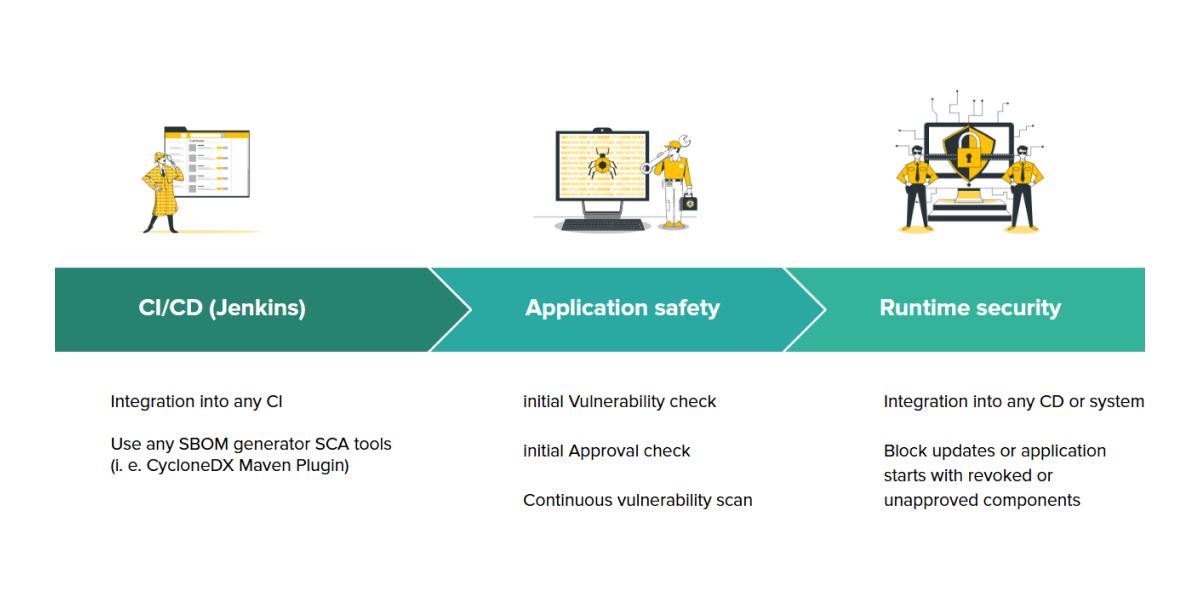
Know your components
- Maintain an open-source list with continuous updates
- Generate SBOMs for open-source applications
- Manage imported SBOMs from software vendors
- Keep an eye on all the open source components in your software and their dependencies
- Tracking of provenance and trust level of each component
Map your component journey
From CI/CD pipeline to apps to production
- Monitor your software vendors’ risk profile
- Track software license compliance
- Monitor and track the dependencies of your app silos and establish cryptographic provenance for your artifact
- Comply with artifact attestation guidelines like in-toto
Some of our integrations
- CI/CD and SCM tools
- Docker and OCI registries
- Several vulnerability scanners (Snyk, Aqua, JFrog)
- Bindings for Java, C++, Python, NodeJS, Go, Rust, PHP
- Digital Signature platforms
 RedHat
 Debian
 Oracle
 Amazon-Linux
 Ubuntu
 Alpine
 AlmaLinux
 Suse
 JFrog
 Jenkins
 GitLab
 Github
 Travis
 Git
 Docker
 Kubernetes
 AWS Lambda
 Python
 Go
 node.js
 php
 Java
 Rust
 Sigstore
 GnuPG
 C++
Can I trust the software in my organization?
AI-driven trust enforcement of applications, and components.